Third Party Risk Management

Vendor relationships and the technology behind them can change after onboarding. We use the Shared Assessments framework to help insurers review and monitor vendors in proportion to their risk, with documented oversight you can demonstrate to boards and regulators.
Can Your Oversight Keep Pace with Changing Vendor Relationships?

Insurers rely on vendors across critical business functions, often with strong review processes already in place. But vendors and their products change over time. New technology and AI capabilities can be introduced after onboarding, creating risks that earlier assessments may not address. Regulatory expectations also continue to evolve. 

It may be time to take a closer look at your third-party risk management (TPRM) program, starting with these questions:

  • Do you know which vendors carry the greatest risk?
  • Has the nature of those relationships changed since onboarding?
  • Can you identify where third-party AI is already in use?
  • Does your current oversight reflect the level of risk each relationship presents?

Where Third-Party Risk Often Comes to Light

Concerns can emerge first through work already underway elsewhere in the organization.

  • AI Governance: Cataloging the AI systems and models in use, including those supplied by outside vendors, can flag high-risk AI vendors that need their own vendor-level assessment.
  • Internal Audit: A dedicated audit or broader risk assessment may identify third-party risk as an area requiring deeper review.
  • Cybersecurity Assessments: Third-party control reviews can surface concerns related to vendor security and control environments.
  • System and Organization Controls (SOC) Reports: SOC reports help organizations evaluate whether a vendor’s controls are implemented and operating effectively, and findings in a report can point to vendors that need closer review.

From there, the decision is whether each vendor relationship is still assessed and monitored at the level of risk it presents, and whether any gaps call for vendor-level reassessment or changes to the program itself.

TPRM Tailored to Where You Are Today

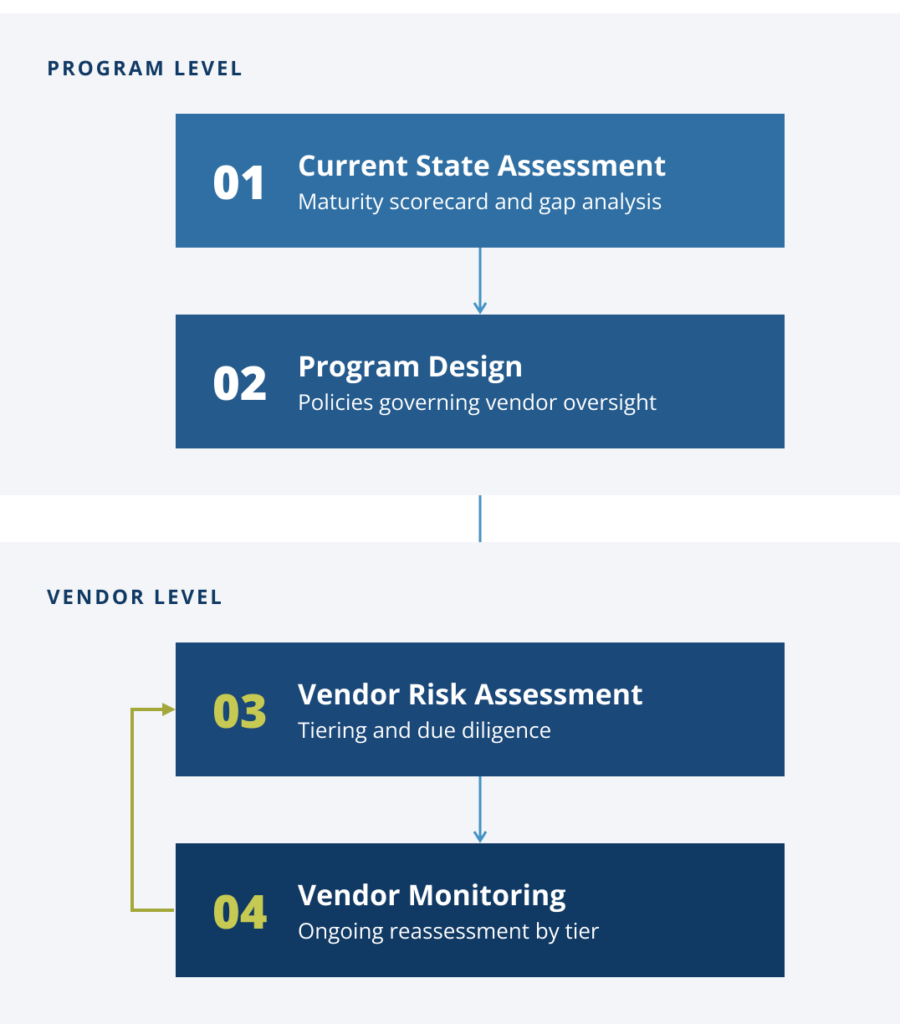
Johnson Lambert’s TPRM offerings address your overall program and the individual vendors within it.

  • Current State Assessment & Maturity Benchmarking: Evaluate your program against the Vendor Risk Management Maturity Model. A maturity scorecard and gap analysis inform a target-state roadmap.
  • Program Design: Define the policies and processes governing vendor oversight, including inventory and tiering, risk assessment and contracting standards, issue management, reporting, and exit planning.
  • Vendor Risk Assessment: Assess individual vendors through inherent-risk tiering, due diligence, control validation, and contract and obligation mapping.
  • Vendor Monitoring: Maintain ongoing oversight through reassessment by vendor tier, continuous monitoring, issue and remediation tracking, and governance reporting.
Download the Brochure

How We Work with Your Team

Right-sized for your organization.

We tailor the work to your current program and the risks your vendor relationships present. Engagements can address a defined need or span the full third-party lifecycle.

Grounded in industry standards.

Johnson Lambert is an official Assessment Firm for the Shared Assessments Program , the organization behind the industry-standard TPRM Product Suite used by more than 15,000 organizations worldwide. That framework guides our approach to scalable, risk-calibrated, defensible, and audit-ready oversight.

No ramp period.

Where we are not your financial statement auditor, our team can work alongside yours on program design and implementation. For existing financial statement audit clients, our role is limited to assessment, findings, and recommendations. Management retains responsibility for remediation, vendor decisions, and risk acceptance.

Focused Industry Experience

Our cybersecurity work is informed by decades of experience serving insurance organizations and nonprofits, with teams that understand the regulatory, operational, and governance issues affecting these sectors.

INSURANCE

40+

years serving insurance organizations, with specialized teams to navigate the industry's unique regulatory expectations, reporting requirements, and operational landscape.

750+

insurance clients nationwide, spanning property and casualty, life, health, title, reinsurance, captives, and MGAs.

5th

largest auditor of P&C insurers nationwide. Deep familiarity with governance and oversight expectations, and active involvement in the AICPA, NAIC, and IASA to keep our teams close to the issues affecting insurance leaders.

NONPROFITS

40+

years of niche-focused experience, with nonprofit teams committed to supporting foundations and associations of various sizes and complexities.

250+

nonprofit clients nationwide, including CDFIs, PACs, member organizations, professional societies, religious, arts & cultural, and social service organizations.

Active involvement

in organizations such as AICPA, NAIC, IASA, ASAE, and Association Forum keeps our team close to the issues affecting insurance and nonprofit leaders.

Meet Your Advisory Team Leaders

Our experts bring insurance-focused experience across third-party risk, AI governance, cybersecurity, SOC reporting, and internal audit.
Is Your TPRM Program Built for Today’s Vendor Environment?

Talk with our third-party risk team about your current approach, how AI may be changing your vendor relationships, and where added assessment or program work may be needed.

Schedule a Conversation