Kim Mobley, CPA, CISA, CISSP
Partner and Advisory Practice Leader

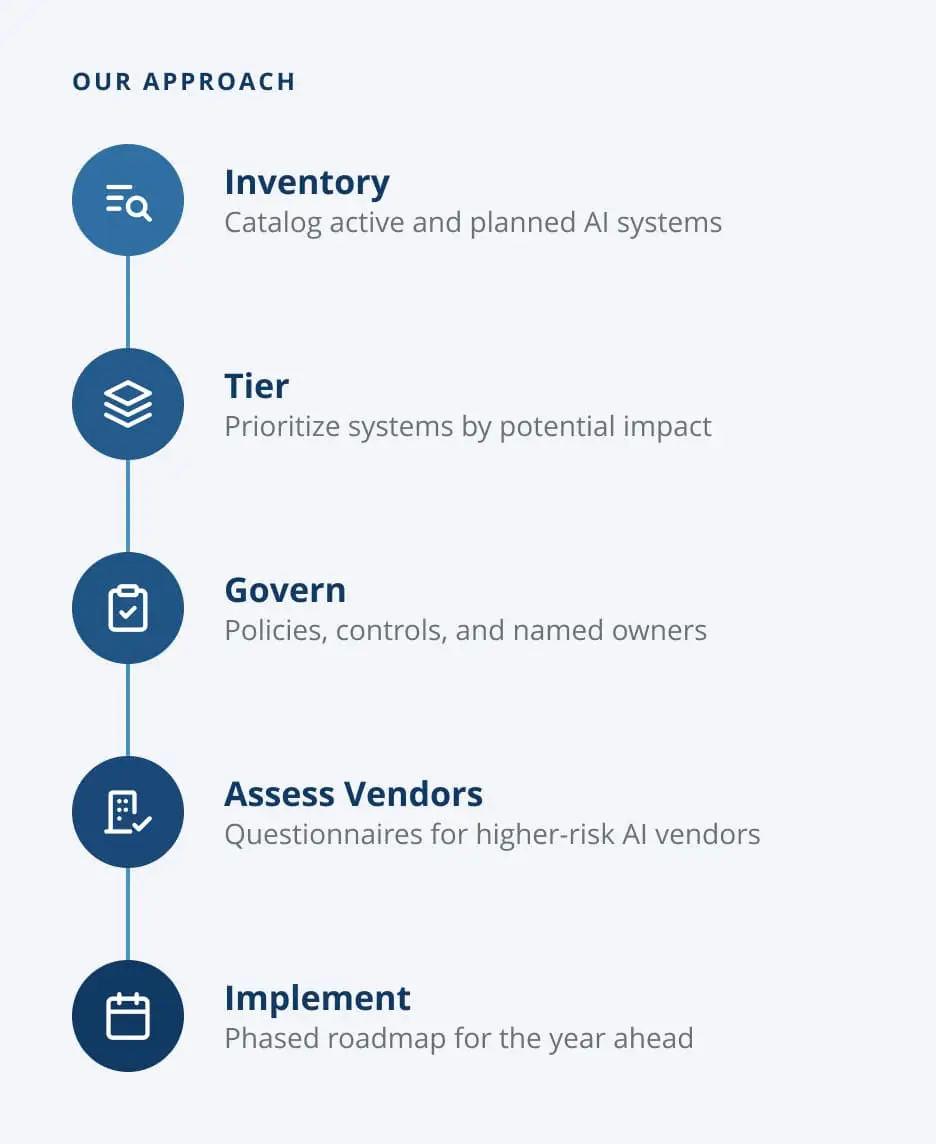
Artificial intelligence often reaches insurers through vendor updates and long-running scoring models before anyone formally reviews it. We help you catalog each system and govern it in proportion to its risk.
Our experts bring insurance-focused experience across third-party risk, AI governance, cybersecurity, SOC reporting, and internal audit.
Learn where auditors look for unapproved AI use and how they test whether controls hold up in day-to-day operations.
READ MORE →
Deepfake-driven claims fraud and AI features added to vendor platforms are two ways AI is widening cyber exposure for insurers.
READ MORE →

Explore how NIST and ISO 42001 can support an insurer’s AI governance program.
READ MORE →

Who is accountable when an AI model produces biased or inaccurate results? Insurance leaders can answer that early, with clear AI policies and a vetting process for every AI solution before it’s approved.
READ MORE →
Our AI governance team works with insurers preparing for the NAIC’s next steps on AI and vendor oversight. Book a complimentary readiness conversation to assess the work your program needs, from inventorying the AI systems you run to implementing the policies and procedures that govern them.
Schedule a ConversationExplore related practices:
|
|
|