October 27, 2026 | 2:00 – 3:00pm ET
Join Johnson Lambert for a practical hour on what independent verification actually requires. We’ll cover the annual requirements shaping cyber programs today, how third party risk management is being tested by the rise of AI embedded in vendor tools, and what a resilience and business continuity plan needs to include to satisfy a board or regulator. The session closes with a candid conversation with a peer executive who manages cyber risk at a public accounting firm, on what it actually takes to stay ahead of these demands with finite time and resources.
What you’ll learn:
This session is ideal for:
General Counsel (GC), Chief Operating Officer (COO), Chief Internal Audit (CIA), CFOs, CIOs, entrepreneurs and other growth-focused leaders
Cybersecurity Awareness Month emphasizes that protecting policyholder data against digital threats requires both vigilance and strategy. Explore recent insights that turn today’s insurance cybersecurity challenges into board-level strategies for governance, compliance, and business continuity.
We help insurers strengthen governance, meet regulatory requirements, and protect critical assets from evolving threats. Our services include:
Cybersecurity Risk Assessment
Benchmark your program against frameworks such as NYDFS Cybersecurity Regulation, NIST CSF 2.0, and CIS Top 18 to identify strengths and gaps.
Artificial Intelligence (AI) Risk Assessment
Evaluate AI governance and implementation processes against the NIST AI Risk Management Framework.
Business Resiliency
Assess recovery and continuity planning, testing strategies, and communication protocols, and build a roadmap for future-state maturity.
Third-Party Risk Management Assessment
Review your vendor management program against regulatory requirements, best practices, and emerging risks.
Program Development & Documentation
Design and implement cybersecurity policies and procedures aligned with your business and regulatory obligations.
Compliance Assessment
Evaluate your cybersecurity program’s compliance to confirm whether proper controls are in place to defend against threats and maintain a strong posture. Services include System and Organization Controls (SOC) for Cybersecurity and Report on Compliance (ROC) NIST 800-171.
You’ll work directly with senior specialists who bring deep regulatory knowledge and decades of insurance and nonprofit experience. They stay engaged from planning through remediation, ensuring complex requirements are translated into practical action.
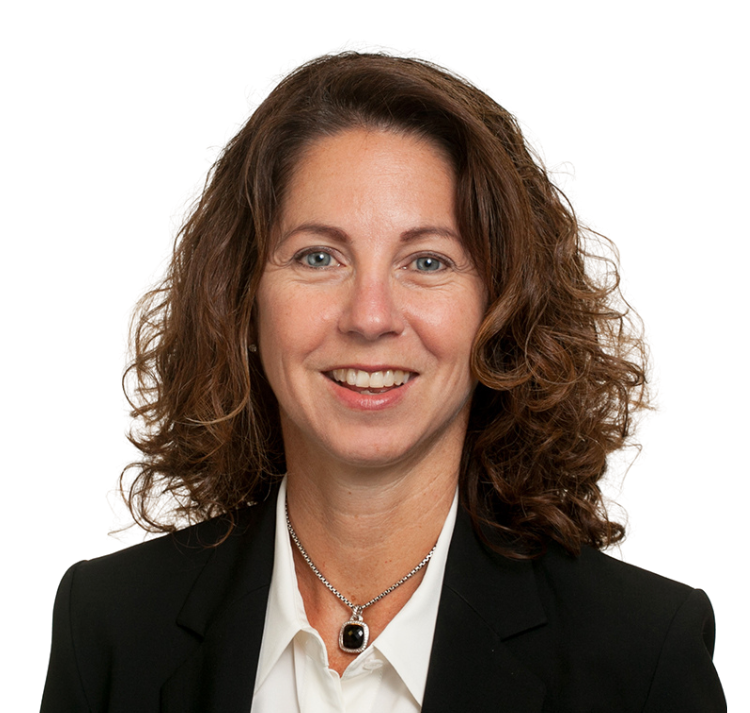
Kim Mobley
Partner


Greg Daniel
Managing Director
Matt Flynn
Senior Manager
Carly Kanwisher
Senior Manager
Cybersecurity is no longer just an IT issue. It is a test of accountability and organizational continuity. The sooner you act, the sooner you can demonstrate oversight, safeguard stakeholders, and stay ahead of emerging risks, which helps build a stronger cyber-safe culture.
Here’s how we help organizations take the next step: